-
The permission question is rarely the real question
-
The deeper issue: permissions are a proxy for data governance
-
Why LinkedIn outreach breaks when API evaluation is shallow
-
The cost of getting company data API evaluation wrong
-
Where okki go vs hunter fits
-
The solution: evaluate the API like you'll own the cleanup
The permission question is rarely the real question
When a RevOps lead asks me, 'What permissions does okki-go require?' I usually answer with another question: what do you want the tool to own after the connection is live?
From the outside, permission screens look like legal boilerplate. The reality is they define your LinkedIn outreach workflow, your company data API pipeline, and how much manual cleanup your SDRs will inherit. I'm a quality and brand compliance manager at a B2B data workflow company. I review every integration and outreach deliverable before it reaches customers—roughly 120 vendor evaluations and campaign QA checks a year. I've rejected about 30% of first-pass drafts because the permission model or data lineage wasn't documented. I want to say the number is higher, but don't quote me on that.
The search query is usually what permissions does okki go require. But that's only the front door. This is why okki go vs hunter comparisons often miss the mark. Hunter is known for email finding and verification. Okki-go is built around agent-native prospecting, waterfall enrichment + intent, and human-in-the-loop outreach. The comparison isn't about which logo wins. It's about which permission and data model fits your process—and which one you can defend in a security review.
The deeper issue: permissions are a proxy for data governance
Most buyers focus on credits and completely miss scopes, refresh cadence, match keys, and audit logs. The question everyone asks is 'How many credits do we get?' The question they should ask is 'What data enters, where does it land, who can export it, and how is it deleted?'
OAuth 2.0 scopes are permission strings that limit what an application can access. That's not a marketing detail; it's the boundary of your risk. According to IETF RFC 6749, scopes let an authorization server define the extent of access granted to a client. In practice, a broad scope like CRM write access is not the same as a narrow read-only enrichment call. One supports automation. The other can rewrite your pipeline.
LinkedIn adds another layer. LinkedIn's API Terms of Use govern access and require compliance with its permissions and partner program requirements (Source: LinkedIn API Terms of Use). So when you ask what permissions okki-go requires, you're really asking how your LinkedIn outreach stays within platform rules while still syncing to your CRM. Depending on your deployment, okki-go may request permissions tied to LinkedIn account connection, CRM read/write, email sending or verification, enrichment APIs, user/profile data, and admin settings. The exact scopes depend on your integrations—confirm them in the admin console and DPA. If a vendor can't explain every scope in plain English, that's a red flag.
Data minimization matters here, too. GDPR Article 5(1)(c) says personal data must be adequate, relevant, and limited to what is necessary. If your company data API pulls every field because 'it might be useful later,' you're not building a pipeline. You're building a liability.
Why LinkedIn outreach breaks when API evaluation is shallow
LinkedIn outreach is not just sending connection requests. It's identity resolution, dedupe, enrichment, intent, sequencing, CRM sync, and suppression. If permissions are too broad, security blocks the rollout. If they're too narrow, the workflow breaks and SDRs go back to spreadsheets.
In a Q1 2025 vendor review, we tested a lower-cost company data API against our internal match requirements. The demo looked clean. The API returned company and contact data fast. Then we audited match keys. It had no durable person or company ID, so every enrichment run created near-duplicates. We spent three weeks—or rather, closer to four once credit and routing data got tangled—reconciling CRM records. That's the TCO nobody puts on the pricing page.
The hidden costs show up later: duplicate records, stale intent signals, bounced emails, confused attribution, and SDR time spent checking whether 'Jon' and 'Jonathan' are the same person. If you push enriched contacts into email sequences, CAN-SPAM applies. The FTC's CAN-SPAM compliance guide requires accurate routing information, a clear opt-out, and honoring opt-outs within 10 business days. Your API evaluation should include how suppression lists sync, not just how many leads it can return.
The cost of getting company data API evaluation wrong
Here's the pattern I see most often. A team saves maybe $200 a month by choosing a lower-cost data API. Then they spend 15–20 SDR hours a month on manual dedupe, plus another chunk of RevOps time fixing CRM sync errors. If an SDR hour is worth $40–60 fully loaded, that 'savings' disappears before the first quarter ends. The cheaper tool was actually the expensive one.
If you're asking what should revenue operations teams evaluate in API company data, start with the list below. Coverage is table stakes. The real scorecard includes:
- Permission model: Least-privilege scopes, admin consent, revocation, and whether LinkedIn, CRM, and email access are separated.
- Data lineage: Source, refresh cadence, retention, deletion, subprocessors, and DPA terms. A SOC 2 Type II report is issued under AICPA Trust Services Criteria; it helps, but it doesn't replace your own review (Source: AICPA).
- Match keys and dedupe: Stable company and person IDs, domain matching, LinkedIn URL normalization, CRM ID mapping, and merge rules.
- Enrichment waterfall and intent: Which sources are used, confidence scores, timestamps, and how intent signals are refreshed. Waterfall enrichment plus intent is useful only if it's explainable.
- Verification and deliverability: No vendor can guarantee 100% deliverability. Evaluate bounce handling, catch-all policy, suppression management, and domain reputation safeguards.
- API mechanics: Rate limits, pagination, webhooks, bulk endpoints, sandbox access, error logging, and audit logs.
- Workflow fit: Human-in-the-loop review, agent-native prospecting, CRM sync direction, sequencing ownership, and who fixes bad data when it appears.
Most teams skip the last two. That's a mistake. The API is not a database in the cloud. It's an operating rhythm. If the rhythm doesn't match your RevOps cadence, you'll pay for it in manual work.
Where okki go vs hunter fits
Hunter usually fits teams that need a focused email finder and verifier. Okki-go usually fits teams that want an agent-native prospecting layer with waterfall enrichment + intent and human-in-the-loop outreach. Many teams run both. The question isn't replacement. It's which system owns the golden record.
If you're comparing okki go vs hunter, score them on the same sheet: permission clarity, dedupe logic, CRM sync, intent refresh, audit logs, and TCO over 12 months. Don't compare a per-seat price to an all-in workflow cost. The $500-per-month tool can turn into $1,200 after security review, integration work, dedupe scripts, and SDR cleanup. The $850 all-inclusive tool may actually be cheaper. That's not a pricing trick. It's total cost thinking.
In my opinion, okki-go's advantage isn't that it does everything. It's that the workflow is designed around agents and humans together. You still need a quality gate. You still need someone to review the message before it goes out. You still need a suppression process. But the permission model should make those controls easier, not harder.
The solution: evaluate the API like you'll own the cleanup
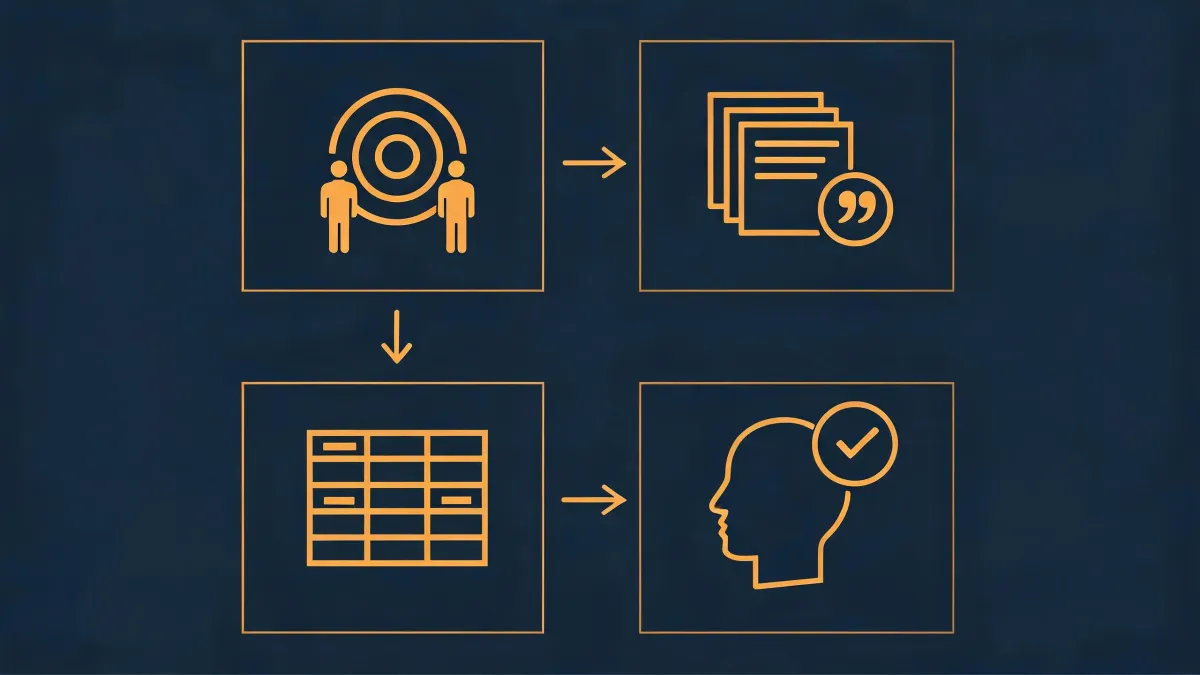
Before you ask what permissions okki-go requires, write down the five things the integration will own: LinkedIn outreach execution, company data API enrichment, CRM sync, intent refresh, and suppression. Then ask which permissions are truly necessary for each.
For a company data API evaluation, run a 30-day pilot with real CRM data. Measure match rate, duplicate rate, enrichment coverage, intent freshness, API latency, and SDR time saved. Include security review hours. Include RevOps reconciliation hours. Include the cost of a bad email send. Then calculate TCO.
If you ask me, the right vendor isn't the one with the longest feature list. It's the one whose permission model you can explain to your security team, whose data lineage you can trace, and whose failures you can clean up without a six-week fire drill. That's how you choose between okki-go and Hunter without buying a future problem.
Permissions are not fine print. They're the shape of your outbound workflow.